Optimizing Image Pull Performance in Kubernetes: Registries, Caching, and imagePullPolicy
Intermediate · 7 min read
Key takeaways
- Leverage image caching and choose the right imagePullPolicy to reduce image pull times in Kubernetes.
- Regularly clean up unused images to free up disk space and maintain optimal performance.
- Consider using a registry mirror or private registry for high availability and improved performance.
- Optimize image size and use CDNs to further enhance the speed and efficiency of image pulls.
The Problem
One of the most common pain points in Kubernetes deployments is the time it takes to pull container images. This delay can significantly impact the overall performance and responsiveness of your application, especially during frequent updates or scaling events. For example, imagine a DevOps team at a fast-growing e-commerce platform. They need to deploy new features and bug fixes quickly, but every time they update their application, the deployment process takes several minutes due to slow image pulls. This not only slows down the development cycle but also impacts the user experience, as the application may be unresponsive during these updates.
Optimizing image pull performance is crucial for maintaining a smooth and efficient CI/CD pipeline. By understanding and implementing the right strategies, you can significantly reduce the time it takes to pull images, leading to faster deployments and a more responsive application.
Core Concepts
Before diving into the specifics, let’s cover some fundamental concepts related to container image management in Kubernetes.
Container Registries
A container registry is a service that stores and distributes container images. Popular container registries include Docker Hub, Google Container Registry (GCR), Amazon Elastic Container Registry (ECR), and Azure Container Registry (ACR). These registries allow you to push, store, and pull container images, making them available for use in your Kubernetes clusters.
Image Caching
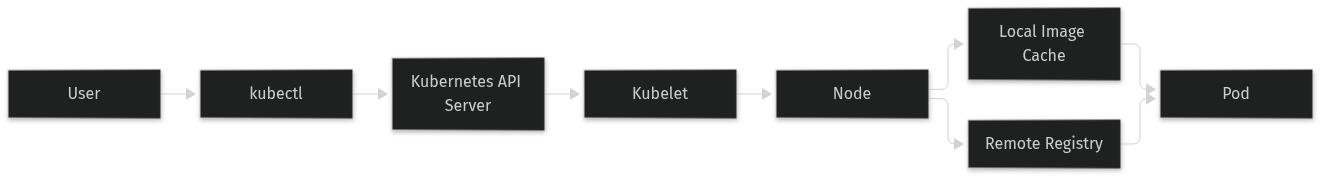
Image caching is the process of storing frequently used container images on the nodes in your Kubernetes cluster. When a pod is created, the node first checks if the required image is already cached locally. If it is, the node uses the cached image, bypassing the need to pull the image from the remote registry. This can significantly reduce the time it takes to start a pod, especially in environments with high latency or limited bandwidth.
imagePullPolicy
The imagePullPolicy is a Kubernetes setting that determines when a container image should be pulled from the registry. There are three possible values:
- Always: The image is always pulled from the registry, even if it is already present locally.
- IfNotPresent: The image is pulled only if it is not already present locally.
- Never: The image is never pulled from the registry; it must be present locally.
How It Works
When a pod is created in Kubernetes, the following steps occur to determine whether and how to pull the container image:
- The kubelet, which runs on each node, receives the pod specification and checks if the required image is already present on the node.
- If the image is not present, the kubelet will attempt to pull the image from the specified registry, based on the
imagePullPolicy. - If the image is already present and the
imagePullPolicyis set toIfNotPresentorNever, the kubelet will use the local image. - Once the image is available, the kubelet creates the container and starts the pod.
By leveraging image caching and choosing the appropriate imagePullPolicy, you can optimize the image pull process and reduce the time it takes to start pods.
Prerequisites
Before you begin, make sure you have the following:
- A running Kubernetes cluster (version 1.20 or later)
- kubectl installed and configured to interact with your cluster
- Access to a container registry (e.g., Docker Hub, GCR, ECR, ACR)
- A basic understanding of Kubernetes and container orchestration
Hands-On Walkthrough
In this section, we’ll walk through a step-by-step example of optimizing image pull performance using image caching and the imagePullPolicy.
Step 1: Create a Sample Application
First, let’s create a simple Nginx application. Save the following YAML manifest as nginx-deployment.yaml:
apiVersion: apps/v1
kind: Deployment
metadata:
  name: nginx-deployment
spec:
  replicas: 3
  selector:
    matchLabels:
      app: nginx
  template:
    metadata:
      labels:
        app: nginx
    spec:
      containers:
      - name: nginx
        image: nginx:latest
        imagePullPolicy: IfNotPresent
        ports:
        - containerPort: 80
This manifest defines a deployment with three replicas of an Nginx container. The imagePullPolicy is set to IfNotPresent, meaning the image will only be pulled if it is not already present on the node.
Step 2: Deploy the Application
Deploy the application using the following command:
kubectl apply -f nginx-deployment.yamlThis will create the deployment and start the pods. If the Nginx image is not already present on the nodes, it will be pulled from the registry.
Step 3: Verify the Image Cache
To verify that the image is being cached, you can check the images on the nodes. First, get the list of nodes in your cluster:
kubectl get nodesThen, SSH into one of the nodes and run the following command to list the cached images:
sudo crictl imagesYou should see the Nginx image listed. If you redeploy the application, the image will be used from the cache, and the pods will start much faster.
Verifying It Works
To confirm that the image is being pulled from the cache, you can monitor the pod creation process. Use the following command to watch the pod events:
kubectl get pods -wWhen you redeploy the application, you should see the pods starting without any image pull events. This indicates that the image is being used from the cache.
Common Mistakes
Here are some common mistakes to avoid when optimizing image pull performance:
- Using
imagePullPolicy: Alwaysunnecessarily: This can lead to increased latency and network usage, as the image is always pulled from the registry, even if it is already present locally. UseIfNotPresentorNeverwhen appropriate. - Not cleaning up unused images: Over time, the image cache can fill up with unused images, leading to disk space issues. Regularly clean up unused images using tools like
kube-image-cleaner. - Ignoring registry rate limits: Some registries, like Docker Hub, have rate limits for image pulls. Exceeding these limits can result in failed deployments. Consider using a private registry or a registry mirror to mitigate this issue.
Going Further
Once you have a good understanding of the basics, you can explore more advanced topics and production considerations:
Scaling and High Availability
As your application scales, you may need to consider the impact of image pulls on your cluster’s performance. To ensure high availability, you can use a registry mirror or a private registry to distribute the load and reduce the dependency on a single external registry.
Security
Security is a critical aspect of container image management. Ensure that your images are signed and verified using tools like Notary or TUF. Additionally, use secure connections (HTTPS) to communicate with your registries to prevent man-in-the-middle attacks.
Performance Tuning
For further performance optimization, consider the following:
- Use a content delivery network (CDN): Some registries offer CDN support, which can significantly reduce the latency and improve the speed of image pulls.
- Optimize image size: Smaller images take less time to pull and require less storage. Use multi-stage builds and minimal base images to reduce the size of your container images.
- Pre-pull images: In some cases, you may want to pre-pull images onto the nodes before deploying the application. This can be done using a DaemonSet or a custom script.
Alternative Approaches
There are alternative approaches to managing container images, each with its own trade-offs:
- Registry Mirrors: Use a local or on-premises registry mirror to cache images and reduce the dependency on external registries. This can improve performance but requires additional infrastructure and maintenance.
- Private Registries: Host your own private registry to store and manage your images. This provides more control and security but also adds complexity and overhead.
- Third-Party Solutions: Consider using third-party solutions like Harbor, Quay, or JFrog Artifactory, which offer advanced features for image management, including caching, security, and access control.
Cleanup
To remove the resources created in this tutorial, use the following commands:
kubectl delete -f nginx-deployment.yamlThis will delete the deployment and all associated pods. You can also clean up any unused images on the nodes using the following command:
sudo crictl rmi --pruneArchitecture
References
This article was written with AI assistance.